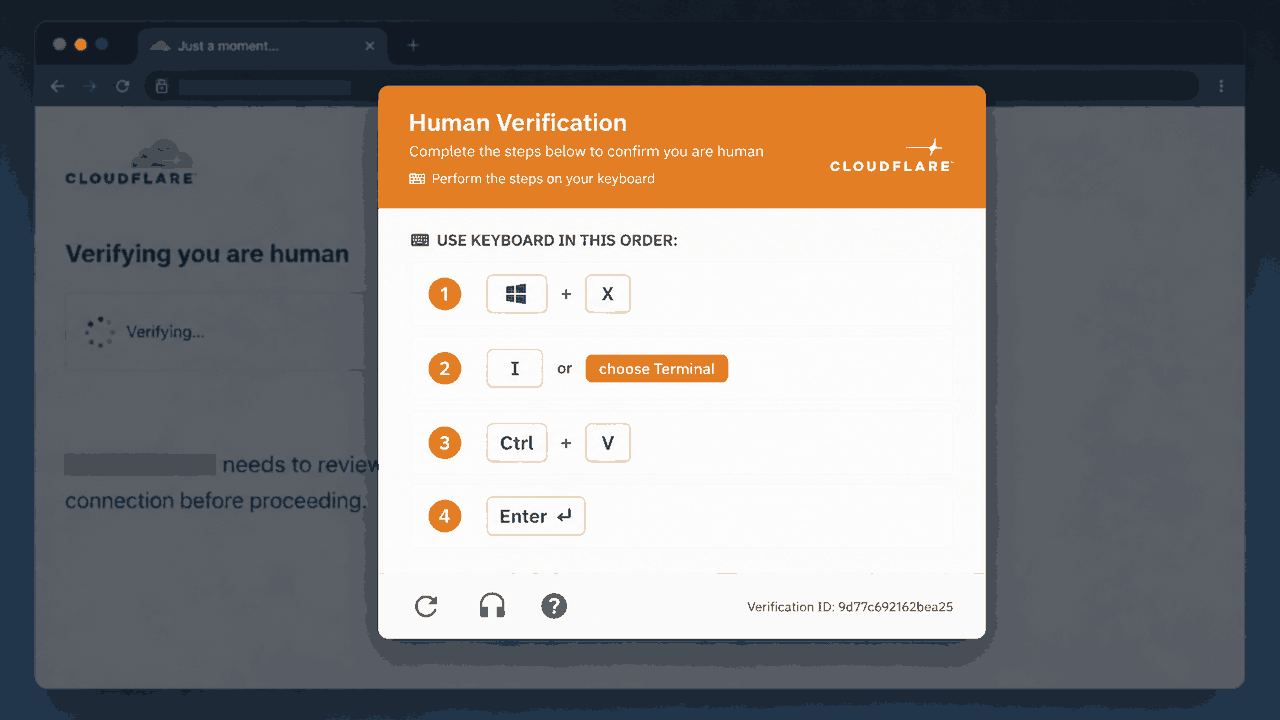
Another day, another 1,738 compromised websites: ClickFix keeps leaning on EtherHiding for C2
ClickFix keeps leaning on EtherHiding for C2 - combined with a prior investigation, this now accounts for over 3,500 compromised sites.
ClickFix keeps leaning on EtherHiding for C2 - combined with a prior investigation, this now accounts for over 3,500 compromised sites.
A second EtherHiding contract, a funding link, and a fully revalidated victim count: 1,829 confirmed hacked websites across two distinct kit families.
A JScript backdoor persists as a WMI ActiveScriptEventConsumer with no file on disk, resolving its C2 address by reading Ethereum smart-contract storage.
A ClickFix DLL side-load traced through a Polygon smart contract (EtherHiding) to 18 C2 domains and 153 confirmed hacked sites across three operators.
FakeNet-NG's WinDivert driver wouldn't load on my ARM Windows box, so I built feintnet: a single Go binary that fakes DNS, TLS, and C2 for malware analysis.
Five-stage ClickFix chain reversed statically - game decoy, bitmap stego, custom ConfuserEx, bespoke byte cipher, and StealC v2 with blockchain-rotated C2.
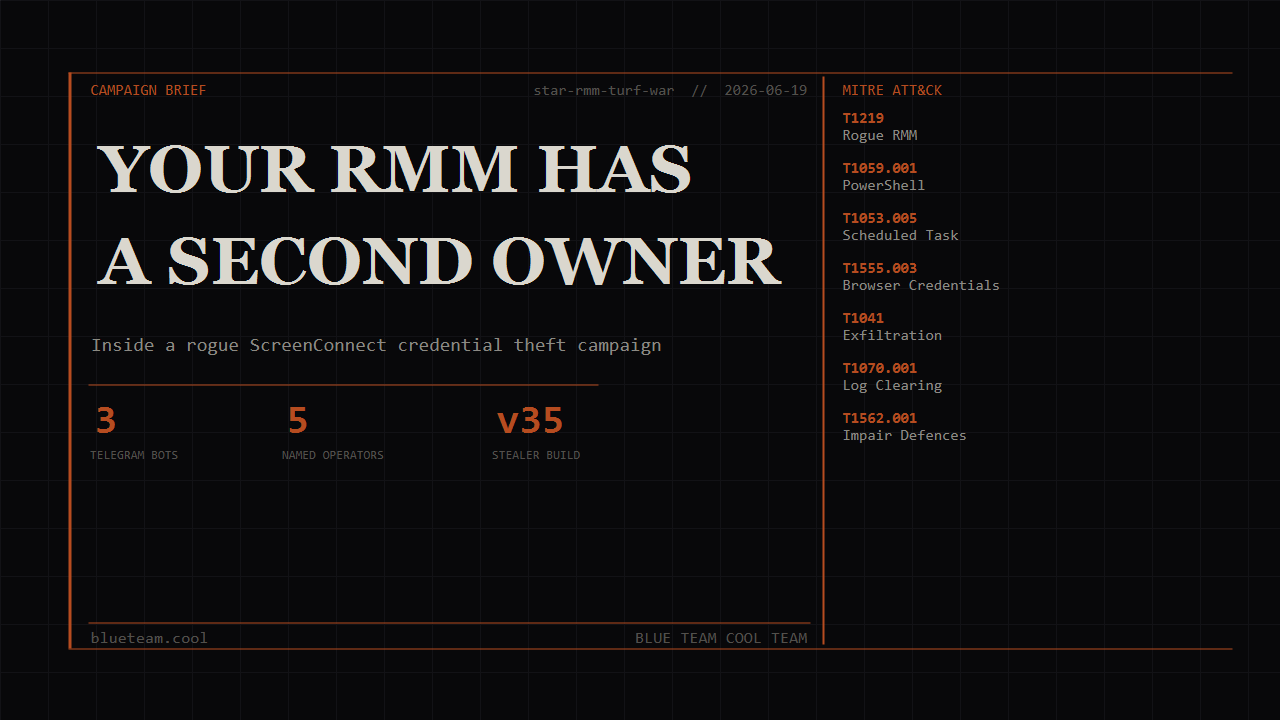
Three Telegram bots, five named operators, a 3,000-line competitor eviction script -- a newly onboarded host had been compromised for months before the customer onboarded it.
25 finger commands over approximately 30 days, three ClickFix families, one TCP/79 delivery vector: IronPython loader, Python RAT lspy, and a pre-positioned DigitalOcean staging cluster.
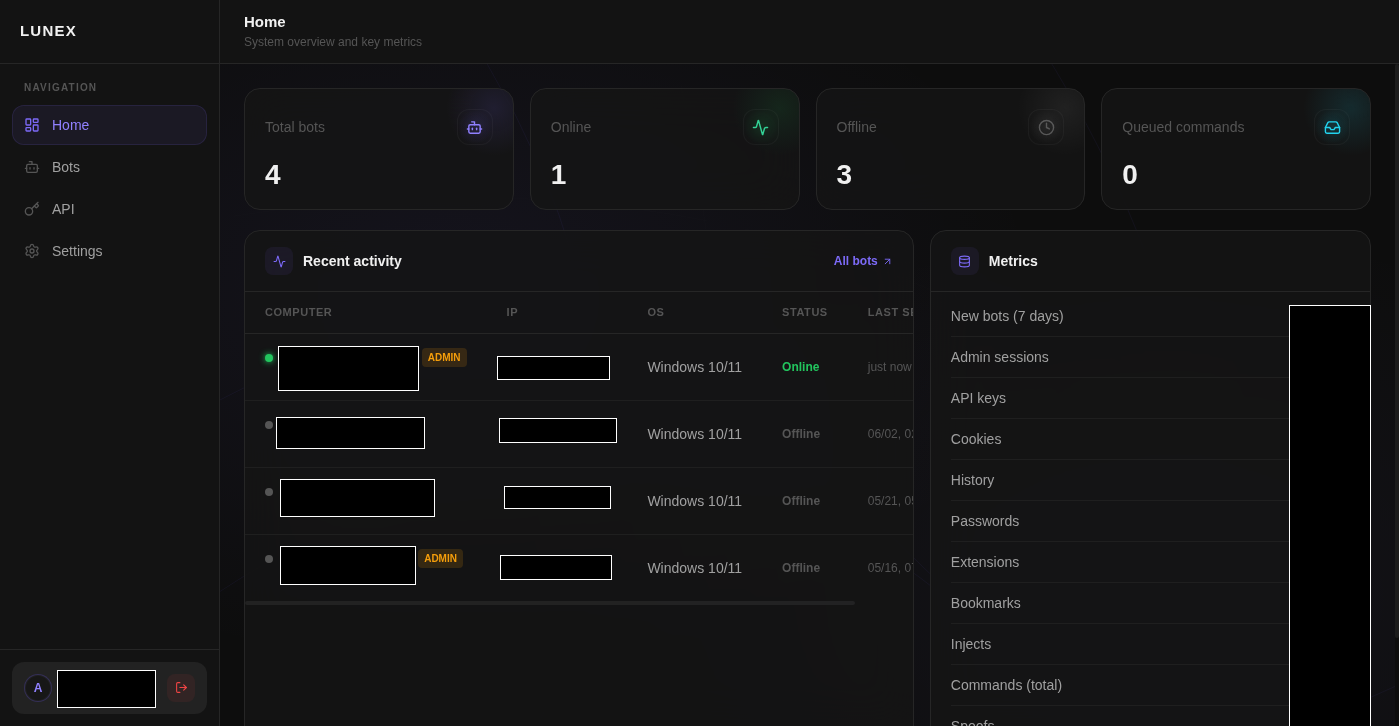
OSINT follow-up to the ClickFix/CAPTCHA campaign: six confirmed Lunex stealer C2 panels across five countries, including a Cloudflare-hidden instance on a Google-impersonating domain. Cookie theft, credential harvesting, real-time JavaScript injection, browser spoofing, and full remote browser control -- documented from the observable panel interface.
A compromised WordPress site, eleven hundred lines of IIS logs, a two-stage binary-encoded webshell, and six attempts to deploy a gsocket reverse shell.